Experts said the notification was akin to a ransom note (Picture: AFP)
Asos has warned shoppers to be wary of any ‘unexpected’ phone calls after being sent a push alert saying the fashion giant had been ‘hacked’.
Shoppers were sent a phone notification from the official Asos app on Tuesday morning saying that the online retailer had been ‘hacked’.
Asos,which has 16.5million customers, told shoppers in an email sent this morning that ‘some personal information,including names and contact details’ was accessed.
The BBC reports that the data includes names,addresses,phone numbers,emails and even what they search on the website,like ‘Asos petite’.
Asos added in the email,seen by Metro,that no payment card information or account passwords were nabbed.
The third party did access ‘certain non-personal account-related information’ but did not elaborate.
The email said: ‘We’re sorry for the unauthorised notification some of you received on October 6 and any uncertainty this caused.’
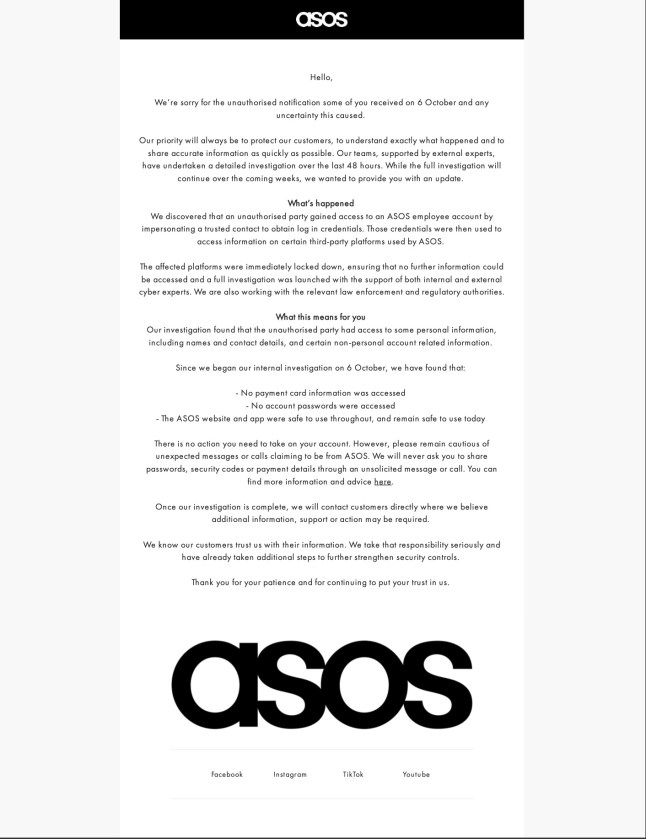
The email sent to Asos customers today (Picture: Asos)
The email continued: ‘There is no action you need to take on your account.
‘However,please remain cautious of unexpected messages or calls claiming to be from ASOS.
‘We will never ask you to share passwords,security codes or payment details through an unsolicited message or call. You can find more information and advice here.’
Experts told Metro that criminals could be masquerading as Asos to exploit worries about data being exposed,called ‘phishing scams’.
Texts about resetting passwords may end with a phone call and the scammer asking to confirm the victim’s card details or login.
Some look-alike texts or emails might include links to websites that install shady software called malware,which steals users’ personal details.
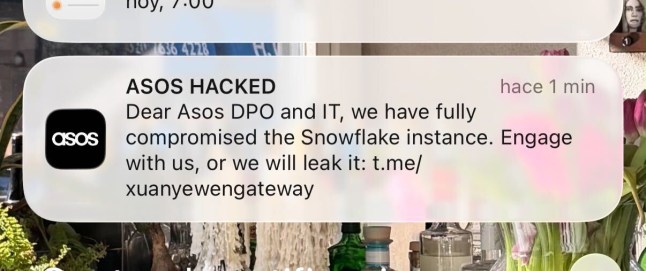
The notification,while sent via the Asos app,was not from the retailer
Asos said in a Q&A about the notification that it is not asking users to reset their passwords and is not sending out app notifications.
Tomas Stamulis,chief security officer at the cybersecurity software company Surfshark,told Metro that Asos shoppers should keep an eye out for any odd communication from other phoney companies,too.
‘Customers need to be wary of any communications from banks and credit card companies offering to protect accounts following the attack,as it could well be scammers trying to feed on the fear,’ Stamulis said.
‘If you are worried that you may have been impacted,change your passwords and keep a close eye on your accounts for any suspicious activity.
‘If you spot anything suspicious,get in touch with your providers proactively using the verified numbers on their websites.’
Asos now faces a crisis in trust,experts say (Picture: AFP)
Asos said that initial findings from its investigation found that an ‘unauthorised party gained access to an Asos employee account by impersonating a trusted contact to obtain login credentials’.
‘Those credentials were then used to access information on certain third-party platforms used by Asos.’
Such a swindle is called a ‘social engineering scam’,Andrew Northage,partner,regulatory and compliance at the law firm Walker Morris,told Metro,where people gain a person’s trust to get personal and financial information.
‘People remain one of the most common routes into an organisation,’ he said.
‘As businesses become more connected,a compromise in one part of the chain can quickly have wider consequences,even where core systems remain secure.’
Northage said that with basic customer information in the hands of hackers,Asos’ problem now is restoring the public’s trust in it.
Shoppers have been asked by experts to reset their passwords just in case (Picture: LightRocket)
Aras Nazarovas,a senior information security researcher at Cybernews,feels the same way.
Shoppers were notified about the hack by the cyber criminals on Tuesday – Asos’ email addressing the situation was sent Thursday.
‘While this might be an attempt to manage public reputation,it should have come sooner,rather than leaving the situation to speculation,’ he says.
‘Customers are entitled to know what personal information was accessed and what steps to take to manage the situation.’
Get in touch with our news team by emailing us at .
For more stories like this,check our news page.
© OfficialAffairs